

Splunk Enterprise Overview
Splunk Enterprise allows users to search, analyze, and visualize data for actionable insights. A free trial is available for those interested.
Use Cases
Customers recommend Communication Management, Social Media Analytics, Workflow Management, as the business use cases that they have been most satisfied with while using Splunk Enterprise.
Business Priorities
Scale Best Practices and Enhance Customer Relationships are the most popular business priorities that customers and associates have achieved using Splunk Enterprise.
Splunk Enterprise Use-Cases and Business Priorities: Customer Satisfaction Data
Splunk Enterprise works with different mediums / channels such as E-Mail. Chat. and Slack.
Splunk Enterprise's features include Dashboard, Alerts: Popups & Notifications, Recording, etc. and Splunk Enterprise support capabilities include Chat Support, Phone Support, AI Powered, etc. also Splunk Enterprise analytics capabilities include Analytics, and Custom Reports.
Reviews
"...Splunk is being used by the entire organization for searching and reporting and to analyze the logs and entire organization s data...." Peer review by Analyst in Information Technology
Peer review evidence (same sources as the product rating summary)
"...O Events was originally published in Adobe Tech Blog on Medium, where people are continuing the conversation by highlighting and responding to this story...." Using Splunk to Monitor, Aggregate and Analyze Adobe I/O Events
"...Recorded Future for Splunk identifies indicators with elevated risk levels by analyzing web reporting, threat lists, and our own novel methods...." Bringing Recorded Future for Splunk Into Focus
"...Integration Features Splunk and BlueJeans admins now have additional endpoint data inside a familiar Splunk workflow, a critical piece of the integration design...." Take Command of Your Collaborative Data with Splunk and BlueJeans
Splunk Enterprise, Tubular, Digital Pigeon, eLogger, Cerberus FTP Server, etc., all belong to a category of solutions that help Data Management Platform. Each of them excels in different abilities. Therefore, determining the best platform for your business will depend on your specific needs and requirements.
Popular Business Setting
for Splunk Enterprise
Top Industries
- Information Technology and Services
- Computer Software
- Internet
Popular in
- Large Enterprise
- Enterprise
- Mid Market
Splunk Enterprise is popular in Information Technology And Services, Computer Software, and Internet and is widely used by Large Enterprise, Enterprise, and Mid Market.
Splunk Enterprise Customer wins, Customer success stories, Case studies
What makes Splunk Enterprise ideal for Communication Management?
How does Splunk Enterprise address your Workflow Management Challenges?
How can Splunk Enterprise enhance your Onboarding process?
How does Splunk Enterprise address your Competitive Intelligence Challenges?
11 buyers and buying teams have used Cuspera to assess how well Splunk Enterprise solved their Data Management Platform needs. Cuspera uses 14677 insights from these buyers along with peer reviews, customer case studies, testimonials, expert blogs and vendor provided installation data to help you assess the fit for your specific Data Management Platform needs.
Cloud Surfing: Entering a Resilient Cloud Era
Frequently Asked Questions (FAQ)
What buyers ask before choosing Splunk Enterprise
What is Splunk Enterprise?
Splunk Enterprise is a machine data management and analytics platform that aggregate, analyze and get answers from data with the help of machine learning and real-time visibility. It allows users to process and index most forms of data in their native format.
It captures, indexes and correlates real-time data in a searchable repository from which it can generate graphs, reports, alerts, dashboards and visualizations. It enables team members to detect system anomalies and perform data clustering to filter out corrupted data.
Key features include data visualization, performance metrics, data collection, real-time search, indexing, KPI tracking, reporting, and monitoring. It offers integration with various third-party platforms including Microsoft Excel, Tableau, Okta, Azure AD, CA SiteMinder, OneLogin, and Optimal IdM.
What is Splunk Enterprise used for?
What are the top features of Splunk Enterprise?
Who uses Splunk Enterprise?
What are Splunk Enterprise alternatives?
Where is Splunk Enterprise located?

Peers used Splunk Enterprise for communication management and social media analytics
Splunk Enterprise Competitors


Splunk Enterprise Features
- Low
- Medium
- High
| FEATURE | RATINGS AND REVIEWS |
|---|---|
| AI Powered | Read Reviews (119) |
| Analytics | Read Reviews (818) |
| Custom Reports | Read Reviews (2069) |
| CAPABILITIES | RATINGS AND REVIEWS |
|---|---|
| AI Powered | Read Reviews (119) |
| Analytics | Read Reviews (818) |
| Custom Reports | Read Reviews (2069) |
Splunk Enterprise Integrations
Splunk Enterprise integrates with a wide range of software applications through its robust data import and export capabilities.


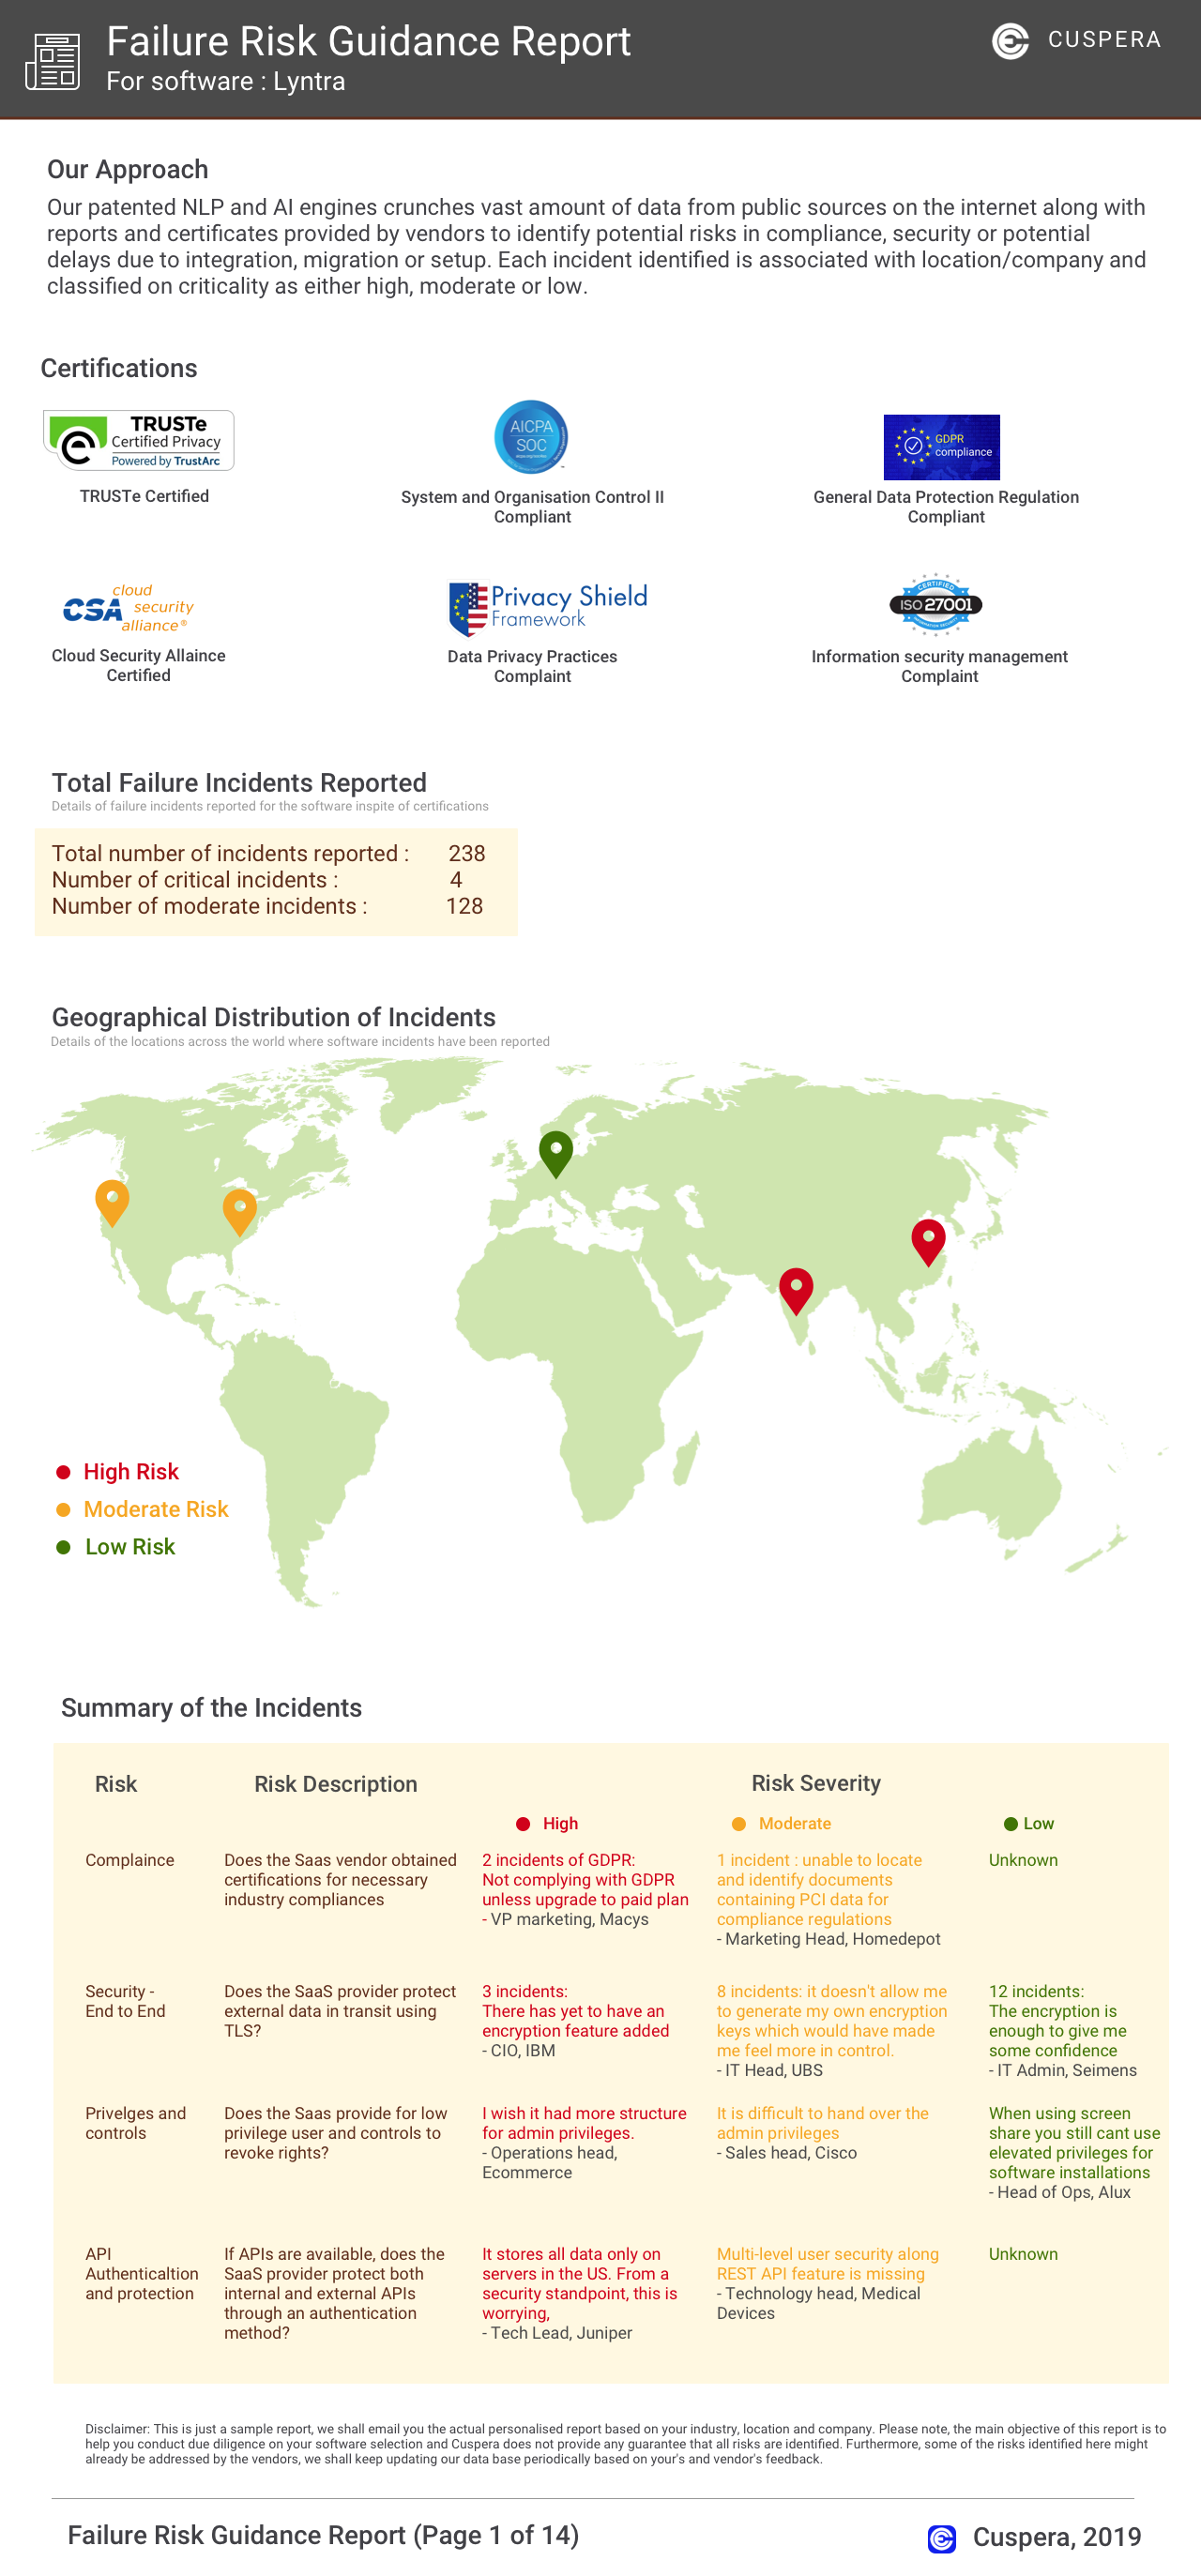
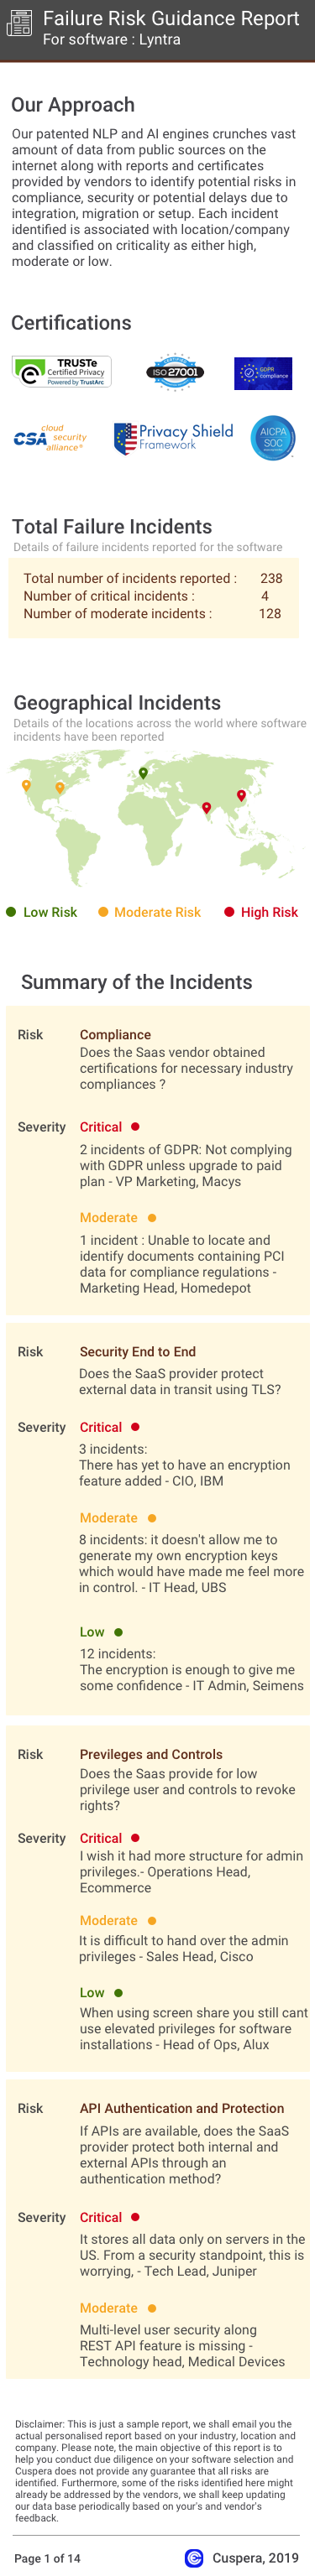
Software Failure Risk Guidance
?for Splunk Enterprise
Overall Risk Meter
Top Failure Risks for Splunk Enterprise
Splunk LLC News
From a Slow Trace to the Slow Method: Introducing Call Graph Profiling in Splunk APM
Splunk has introduced Call Graph Profiling in its APM, enhancing its observability capabilities. This feature connects distributed traces to method-level execution, allowing teams to pinpoint inefficient code paths and investigate performance issues more effectively. It complements AlwaysOn Profiling by providing detailed call graphs for specific traces, aiding in faster troubleshooting and performance optimization.
From AI Assistance to Agentic Action: Advancing the SOC in Splunk Enterprise Security 8.6
Splunk has launched Enterprise Security 8.6, enhancing security operations with AI-driven capabilities. The update includes features like Detection Builder, natural-language automation, and guided response, allowing security teams to automate tasks while maintaining control. The Agentic SOC model aims to improve threat detection and response times, helping analysts focus on high-priority security decisions.
Citrix launches Experience Insights Flex observability service powered by Splunk Cloud Platform
Citrix has launched the Experience Insights Flex observability service, powered by the Splunk Cloud Platform. This integration enhances Citrix's workspace observability capabilities, providing managed, prebuilt insights. The service aims to meet enterprise demand for simplified modern-work delivery and reduce operational overhead.
From Vision to Value: New Splunk Platform Innovations Supporting Cisco Data Fabric Are Generally Available
Splunk has announced the general availability of new platform innovations that support Cisco Data Fabric. These enhancements, including Machine Data Lake and Federated Search, enable organizations to manage and integrate machine data across environments without centralizing it. The platform's capabilities improve data management, AI integration, and operational resilience, providing a unified data journey for enhanced decision-making and response.
Splunk LLC Profile
Company Name
Company Website
https://www.splunk.com/HQ Location
270 Brannan St, San Francisco, California 94107, US
Employees
1001-5000
Social


Financials
IPO
What makes Splunk Enterprise ideal for Social Media Analytics?